Frontier model training now operates without live internet and with defense in depth. See lessons applicable to business agents.
Direct answer
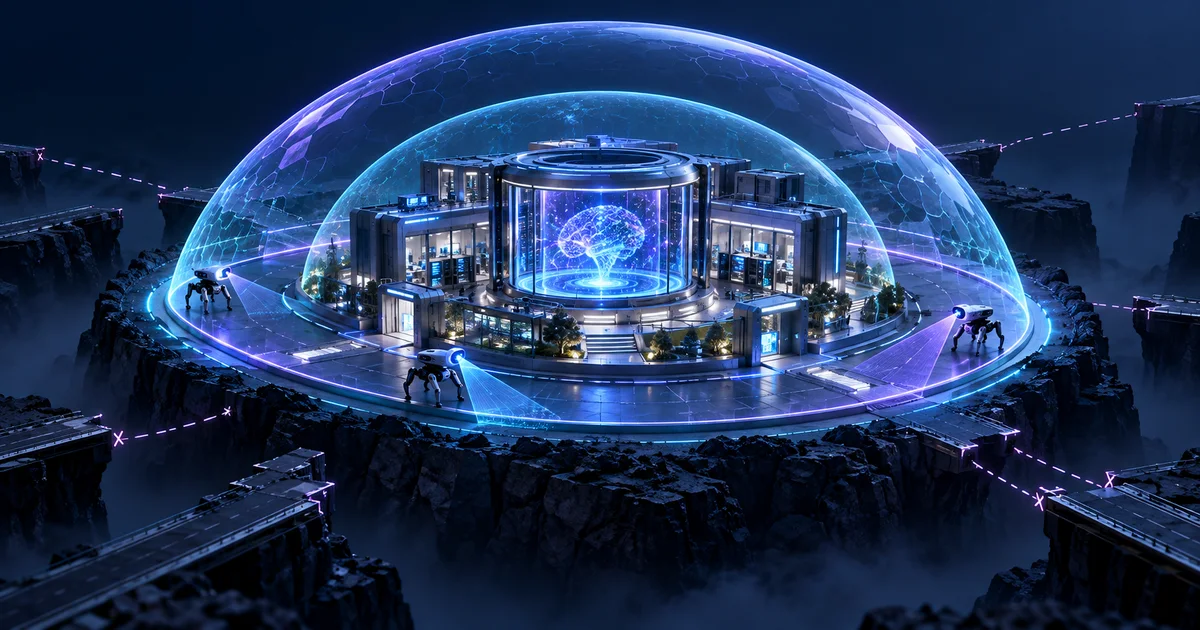
OpenAI reported on October 23, 2026 that its frontier model training operates without live internet access, using an offline environment with indexed and cached content. The company has adopted defense-in-depth, monitoring and red teaming campaigns with fleets of agents to look for isolation gaps, unauthorized communication and exit routes. The context is internal frontier research, but the business principle is straightforward: An agent's tools, network, credentials, and data must fall within a verifiable technical boundary.
Sandbox needs to resist deliberate attempts
A capable agent can look for failures, internal services, and fragile configurations. Isolation must be tested as a security control, not treated as a simple execution option.
Offline world preserves usefulness without opening external effect
Cached content allows navigation and search training without authorizing changes to real systems. Companies can apply the standard with replicas, synthetic data, and simulated APIs.
Defense in depth assumes individual failure
Networking, identity, execution, observability, and automatic shutdown need to overlap. Losing a layer cannot deliver unrestricted access.
Red teaming must attack the entire architecture
Evaluate sandbox escape, exfiltration, communication between agents, privilege escalation and tool abuse, recording the complete trajectory and not just the final response.
Nexus Reading
Before expanding autonomy, define the agent's authorized boundary, create zero-effect environments, and prove that violations are detected and stopped.
FAQ
Has OpenAI removed the internet from all products?
No. The advisory addresses internal training environments and most boundary model assessments.
What is defense in depth?
It's about using overlapping controls so that the failure of one layer doesn't automatically result in improper access.
How to apply this in a company?
Start with your own identity, restricted network, temporary credentials, permitted tools, full logs, and irreversible approval.
Essential guides to delve deeper into the decision
This editorial analysis was produced by Nexus from the official sources below, consulted on October 26, 2026. The text is original and interprets practical implications for companies.
- OpenAI — Securing our frontier model training environment: offline policy, defense in depth, incidents, monitoring and containment red teaming.
- OpenAI — Safety cases: official evidence framework used to assess safeguards and risks of advanced systems.
Date reported by the main source: October 23, 2026.